European Cyber-Strike Targets Fake Visa Sites and Consular Appointment Bot Syndicates
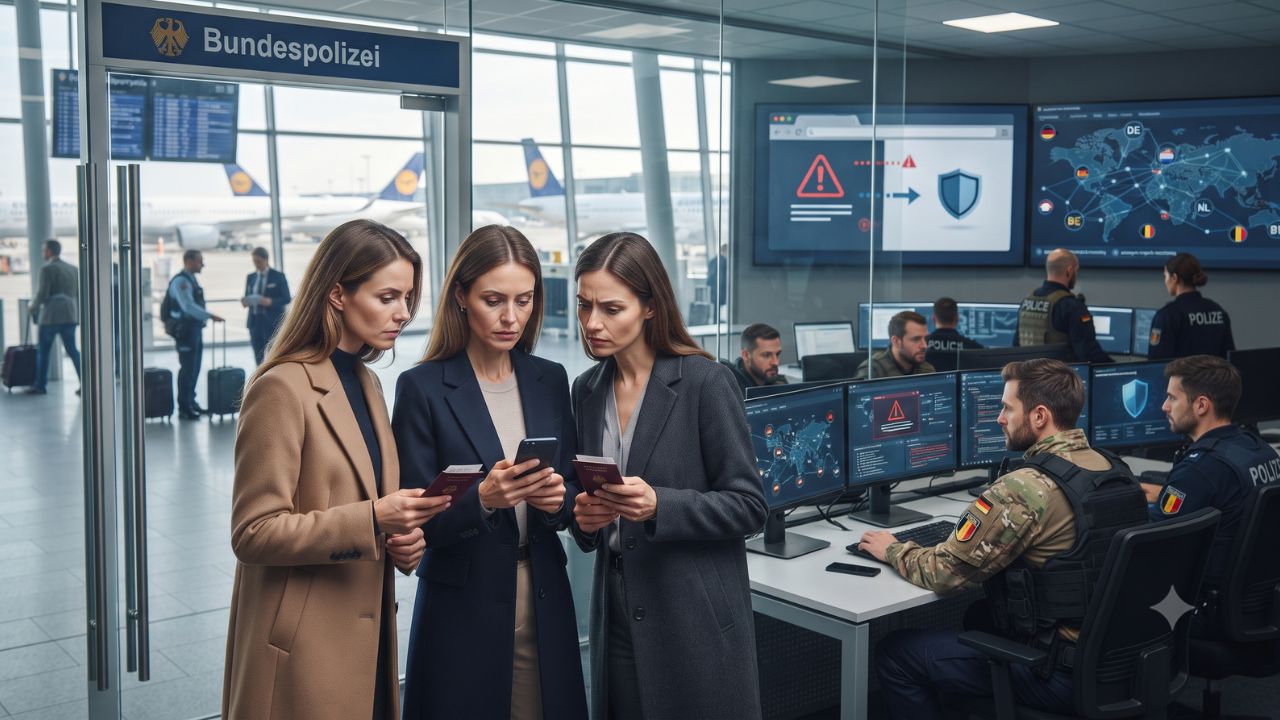
Extracting illicit markups exceeding 500 percent over statutory government fees and hoarding consular appointment slots for black-market resale at upwards of €1,000, international cyber-syndicates targeting digital travel authorizations have triggered an aggressive multinational enforcement offensive across Western Europe. Coordinated through Europol alongside INTERPOL, the joint operation unites Germany’s Federal Criminal Police Office (BKA) and Federal Police, the Netherlands’ National Cyber Security Centre (NCSC) and High Tech Crime Unit, and Belgium’s Federal Computer Crime Unit (FCCU). The coalition targets an industrialized ecosystem of rogue websites that clone official state portals, intercept biometric and passport archives, and exploit consumer confusion surrounding the rollout of the European Entry/Exit System (EES) and upcoming European Travel Information and Authorisation System (ETIAS).
The enforcement operation represents a fundamental tactical evolution in international border security. As global immigration authorities transition from physical visa stamps to cloud-based electronic authorizations—including the US Electronic System for Travel Authorization (ESTA), the UK Electronic Travel Authorisation (ETA), and Canada’s electronic Travel Authorization (eTA)—transnational criminal organizations have established enterprise-level infrastructure to exploit applicants. Operating deceptive domains using .agency, .us, .com, and .org suffixes that mimic official .gov and .europa.eu gateways, these rings siphon millions of euros from travelers while compromising sovereign identity databases and exposing innocent tourists to severe immigration penalties.
Industrialized Deception: The Five-Stage Cyber-Syndicate Architecture
Modern travel authorization fraud has expanded far beyond crude email phishing into sophisticated digital operations. Intelligence collected across the Schengen area demonstrates a five-stage progression that ensnares consumers through automated technical exploitation.
The scheme initiates through aggressive search engine manipulation, where criminal networks outspend public agencies on sponsored keyword advertising to position clone platforms above legitimate government portals. Once travelers land on lookalike portals that mimic official state seals and administrative typography, the second stage captures full passport biographical pages, national identity numbers, home addresses, and credit card data. The third stage imposes extortionate markups, charging anywhere from €150 to over €1,000 for services that are legally free or nominally priced.
| Travel Authorization / Service | Statutory Official Fee | Fraudulent Syndicate Charges | Primary Operational Risk & Traveler Impact |
|---|---|---|---|
| UK Electronic Travel Authorisation (ETA) | £16.00 | $80.00 – $150.00+ | Inflated unauthorized fees; zero verified government submission |
| US Electronic System for Travel Authorization (ESTA) | $40.27 | $100.00 – $200.00+ | Copycat portals; passport data theft; invalid travel status |
| Schengen Consular Appointment Slots | Free / Nominal center fee | €300.00 – €1,000.00+ | Automated bot hoarding; black-market appointment extortion |
| European Entry/Exit System (EES) | Free (€0.00 in-person check) | $50.00 – $150.00 | Fraudulent online pre-registration fees for mandatory physical gates |
| Canada electronic Travel Authorization (eTA) | CAD $7.00 | $60.00 – $120.00+ | Deceptive expedited handling fees on basic automated forms |
| Upcoming ETIAS Authorization (30 EU Nations) | Official €7.00 framework | $75.00 – $180.00 | Fake pre-launch approvals exploiting consumer rollout anxiety |
The fourth stage involves automated appointment hoarding, where criminal syndicates deploy high-speed bot scripts to monopolize available booking calendars at outsourced visa application centers, including VFS Global, TLScontact, and BLS International. Legitimate applicants are locked out of free appointments and forced to purchase slots from illicit social media brokers. Finally, the fifth stage exposes travelers to legal ruin: victims arrive at airport departure gates only to discover that their applications were never submitted, or worse, that rogue intermediaries submitted forged hotel reservations or altered bank statements, resulting in immediate denied boarding and long-term Schengen entry bans.
European Counter-Strike: Three Tactical Enforcement Pillars
Recognizing the cross-border agility of these cyber networks, the trilateral alliance between Germany, the Netherlands, and Belgium has mobilized a three-pillar technical strategy to neutralize fraudulent infrastructure.
Under the first pillar, technical teams execute automated domain name system (DNS) sinkholing and rapid takedowns. Supported by Dutch high-tech cyber units, automated crawlers scan public registries for newly indexed domains pairing terms like schengen, esta, or ees with generic commercial extensions, neutralizing malicious links before they achieve search-engine indexing. The second pillar deploys specialized bot-defense algorithms across visa service provider portals, purging automated scraper scripts and restoring fair queue access for individual applicants.
The third pillar focuses on aggressive financial interdiction. Working directly with European banking regulators and international card networks, German and Belgian investigators trace illicit merchant IDs, freeze IBAN-linked holding accounts, and blacklist associated cryptocurrency addresses. This financial choke point enables victimized travelers to pursue rapid chargebacks while severing the revenue flows that sustain syndicate server networks. Travelers seeking authentic European entry rules are urged to consult the European Union Official Travel Portal directly.
Expert Analysis: Digital Border Friction and Identity Extortion Economics
The emergence of commercial visa-spoofing cartels exposes an unintended byproduct of the international community's push toward paperless border controls. While digital authorizations reduce processing overhead for border agencies, they transfer significant data-entry burdens onto individual passengers who lack the technical literacy to distinguish between authorized sovereign portals and predatory lookalikes.
For travelers booking this route, the direct consequence is an operational environment where a single errant web search can result in immediate travel cancellation and identity compromise. When an applicant mistakenly inputs their passport and banking details into an unauthorized portal, paying $150 for a £16 UK ETA or a $40.27 US ESTA, the financial loss is merely the initial symptom. If the fraudulent portal fails to interface with the destination state's immigration databases, the airline’s interactive Advance Passenger Information system will return a "No Board" directive at check-in. The traveler is denied boarding with zero entitlement to airline rebooking or statutory compensation.
The pricing pressure this creates means that legitimate visa application centers and sovereign immigration agencies must absorb higher cybersecurity and verification costs to defend their digital perimeter. Consular processing agencies are forced to implement multi-factor biometric authentication and anti-bot captchas that slow down appointment booking workflows for genuine travelers.
Simultaneously, harvested personal records sold across dark web forums fuel secondary extortion campaigns, where victims receive fraudulent legal notices threatening deportation unless additional fees are paid. By dismantling appointment hoarding cartels and seizing malicious domains, the European cyber coalition is attempting to protect the integrity of the Schengen perimeter before the EES and ETIAS architectures become fully operational across 30 European member states. Further guidance on international cybercrime reporting can be verified through the Federal Criminal Police Office (BKA).
Key Takeaways
- Trilateral Enforcement Alliance: Germany (BKA), the Netherlands (NCSC), and Belgium (FCCU) join Europol and INTERPOL in an offensive against fake visa portals and bot cartels.
- Inflated Fee Exploitation: Rogue operators charge up to $150 for a £16 UK ETA, over $200 for a $40.27 US ESTA, and up to €1,000 for hoarded Schengen visa appointment slots.
- EES Pre-Payment Scams: Fraudulent platforms trick travelers into paying $50 to $150 for fake online EES registrations, despite the official European border system collecting biometrics in person at zero cost.
- Three-Pillar Neutralization: The task force executes automated DNS sinkholing, deploys anti-bot defenses on application portals, and freezes criminal IBAN accounts and payment merchant gateways.
- Severe Passenger Penalties: Victims of fake agency filings face denied airport boarding, stolen identity credentials, and multi-year Schengen entry bans if third-party operators submit forged supporting documents.
FAQ: European Visa Scams and Cyber-Strike 2026
Does the European Entry/Exit System (EES) charge an online registration fee?
No. The official EES records biometric data in person at border control booths at zero cost. Any website demanding online advance payment for EES registration is fraudulent.
How much do official US ESTA and UK ETA authorizations cost?
The official statutory fee for the US ESTA is $40.27, while the UK ETA costs £16. Higher charges indicate unauthorized third-party commercial intermediaries or copycat scams.
Can third-party services guarantee a Schengen visa appointment or approval?
No. Schengen visa appointments should only be booked through official embassy partners (VFS, TLS, BLS), and no external agent can influence diplomatic visa decisions.
What should travelers do if they used a fraudulent visa website?
Contact your financial institution immediately to dispute charges and cancel compromised cards, check official government portals to verify true application status, and report the incident to cyber authorities.
[As borders transition into digital code, passenger vigilance against deceptive web domains remains the primary safeguard against travel disruption and identity theft.]
Related Travel Guides
Disclaimer
This article is for informational and educational purposes only. It does not constitute legal, financial, or professional advice. While we strive to provide accurate and up-to-date information, travel policies, regulations, and conditions change rapidly. Always verify information with official sources before making travel decisions. Nomad Lawyer makes no representations about the accuracy, reliability, completeness, or suitability of the information provided. Readers should consult qualified professionals for advice specific to their circumstances. The views expressed in this article are those of the author and do not necessarily reflect the views of Nomad Lawyer.
Naina Thakur
Contributor & Travel Specialist
Travel enthusiast and legal writer covering visa regulations, responsible tourism, and cultural journeys across global destinations.
Learn more about our team →